Fake SubsPlease Anime Torrents Hide Malware Behind a Genuine VLC Player
Torrents posing as new SubsPlease episodes of Jujutsu Kaisen and Frieren contain a VLC player that loads malware, according to data from a torrent index.
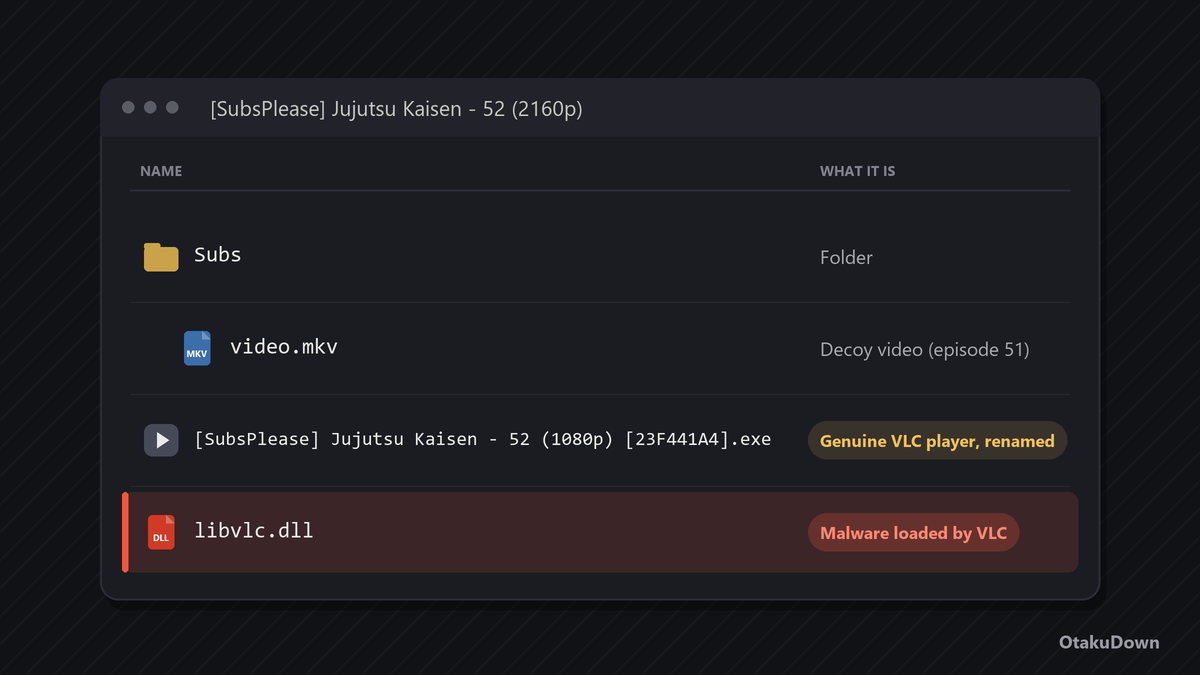
Torrents posing as new episodes of Jujutsu Kaisen and Frieren are being used to spread malware, some of them under the name of SubsPlease, a well-known anime release group. Alongside the video, the torrents include a program named after the episode that runs malicious code when opened.
The findings come from TorrentClaw, a torrent search engine that downloads parts of torrents to check what is inside them, TorrentFreak reported on October 11.
A real player with a poisoned file
TorrentClaw, which launched in February and whose developer says it is largely built and run with AI tools, joins each swarm and downloads about 10 to 20 MB to analyze the video. Suspicious files are checked against the scanning service VirusTotal.
In its late September data, 34 torrents were confirmed as malware. In 31 of them, the torrent contained a program named after a new episode or film, a file called libvlc.dll, and a playable video placed in a subfolder.
The program itself was an unmodified copy of the VLC media player, signed by its developer VideoLAN. When VLC starts, it loads libvlc.dll from the same folder. In these torrents that file was malicious, and antivirus engines on VirusTotal flag it as a trojan.
Besides Jujutsu Kaisen and Frieren, the fakes used the names of The Boys, Dune: Part Three and Zootopia 2. They carried the labels of SubsPlease and other familiar release names, such as ETHEL and YTS.
TorrentClaw found the 31 torrents between February and August. Of these, 22 came from its own crawler of the BitTorrent network and the rest from Nyaa, The Pirate Bay and TorrentDownload. Fifteen were still active in early October, its developer told TorrentFreak, and one fake Jujutsu Kaisen episode still had 34 seeders.
The numbers are small. TorrentClaw flagged 1,265 of the 687,057 torrents it probed as misleading in some way, under 0.2%, and confirmed 34 as malware.
A stolen Nyaa account
The same method was documented earlier this year by a security researcher who goes by shavitush. In a technical write-up, they describe a torrent titled "[SubsPlease] Jujutsu Kaisen - 52 (2160p)" that appeared on Nyaa around January 29, before episode 52 had aired and at a higher resolution than expected.
According to the researcher, it was uploaded through a stolen Nyaa account, not the group's official one. Inside were a signed VLC program named after the episode, the malicious libvlc.dll and a video file, which turned out to be episode 51. Opening the program played that video as a decoy while the malware ran.
The final payload is an information stealer. It targets saved browser passwords and cookies, Discord, gaming platforms and cryptocurrency wallets, among other data, the researcher writes. They first identified it as Vidar, then updated the write-up after being told it was Rhadamanthys, another known infostealer.
The researcher says another Nyaa account was later used for a similar attempt and has since been taken down.